-
 Introducing AI Trustops: Snyk’s readiness framework for building and maturing secure AI development practice
whitepaper
whitepaper -
 Building AI Trust eBook: Securing code in the age of autonomous development
whitepaper
whitepaper -
 Enterprises need to sharpen up on software supply chain security
News A new report from LevelBlue shows many enterprises are failing on software supply chain security, despite growing risks.
News -
 Cloudflare is cracking down on AI web scrapers
News Cloudflare CEO Matthew Prince said AI companies have been "scraping content without limits" - now the company is cracking down.
News -
 Want to build more secure software? Follow these key memory safe language tips from CISA
News CISA has been pushing for a shift to memory safe languages - now it's published guidance on how developers can make the switch.
News -
 Future-proof your development: The SAST/SCA Buyer’s Guide in the AI Era
whitepaper
whitepaper -
 Taming AI Code: Securing Gen AI Development with Snyk
whitepaper
whitepaper -
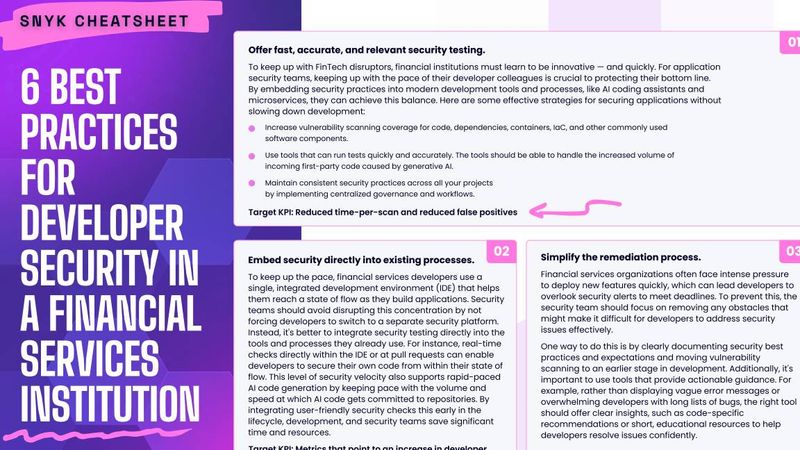 Developer security best practices for FinServ
Whitepaper Developer security in a financial services institution
Whitepaper -
 Application security risk: How leaders can protect their businesses
Application security risk is higher than ever, as new services and expanding attack surfaces put pressure on cyber leaders
-
 Shifting left might improve software security, but developers are becoming overwhelmed
News Developers are becoming overwhelmed amid the 'shift left' in development practices, new research shows.
News -
 CISOs take the back seat as dev teams claim responsibility for application security
News Development and engineering teams are steering security and budget strategies
News -
 The NCSC wants developers to get serious on software security
News The NCSC's new Software Security Code of Practice has been welcomed by cyber professionals as a positive step toward bolstering software supply chain security.
News


