-
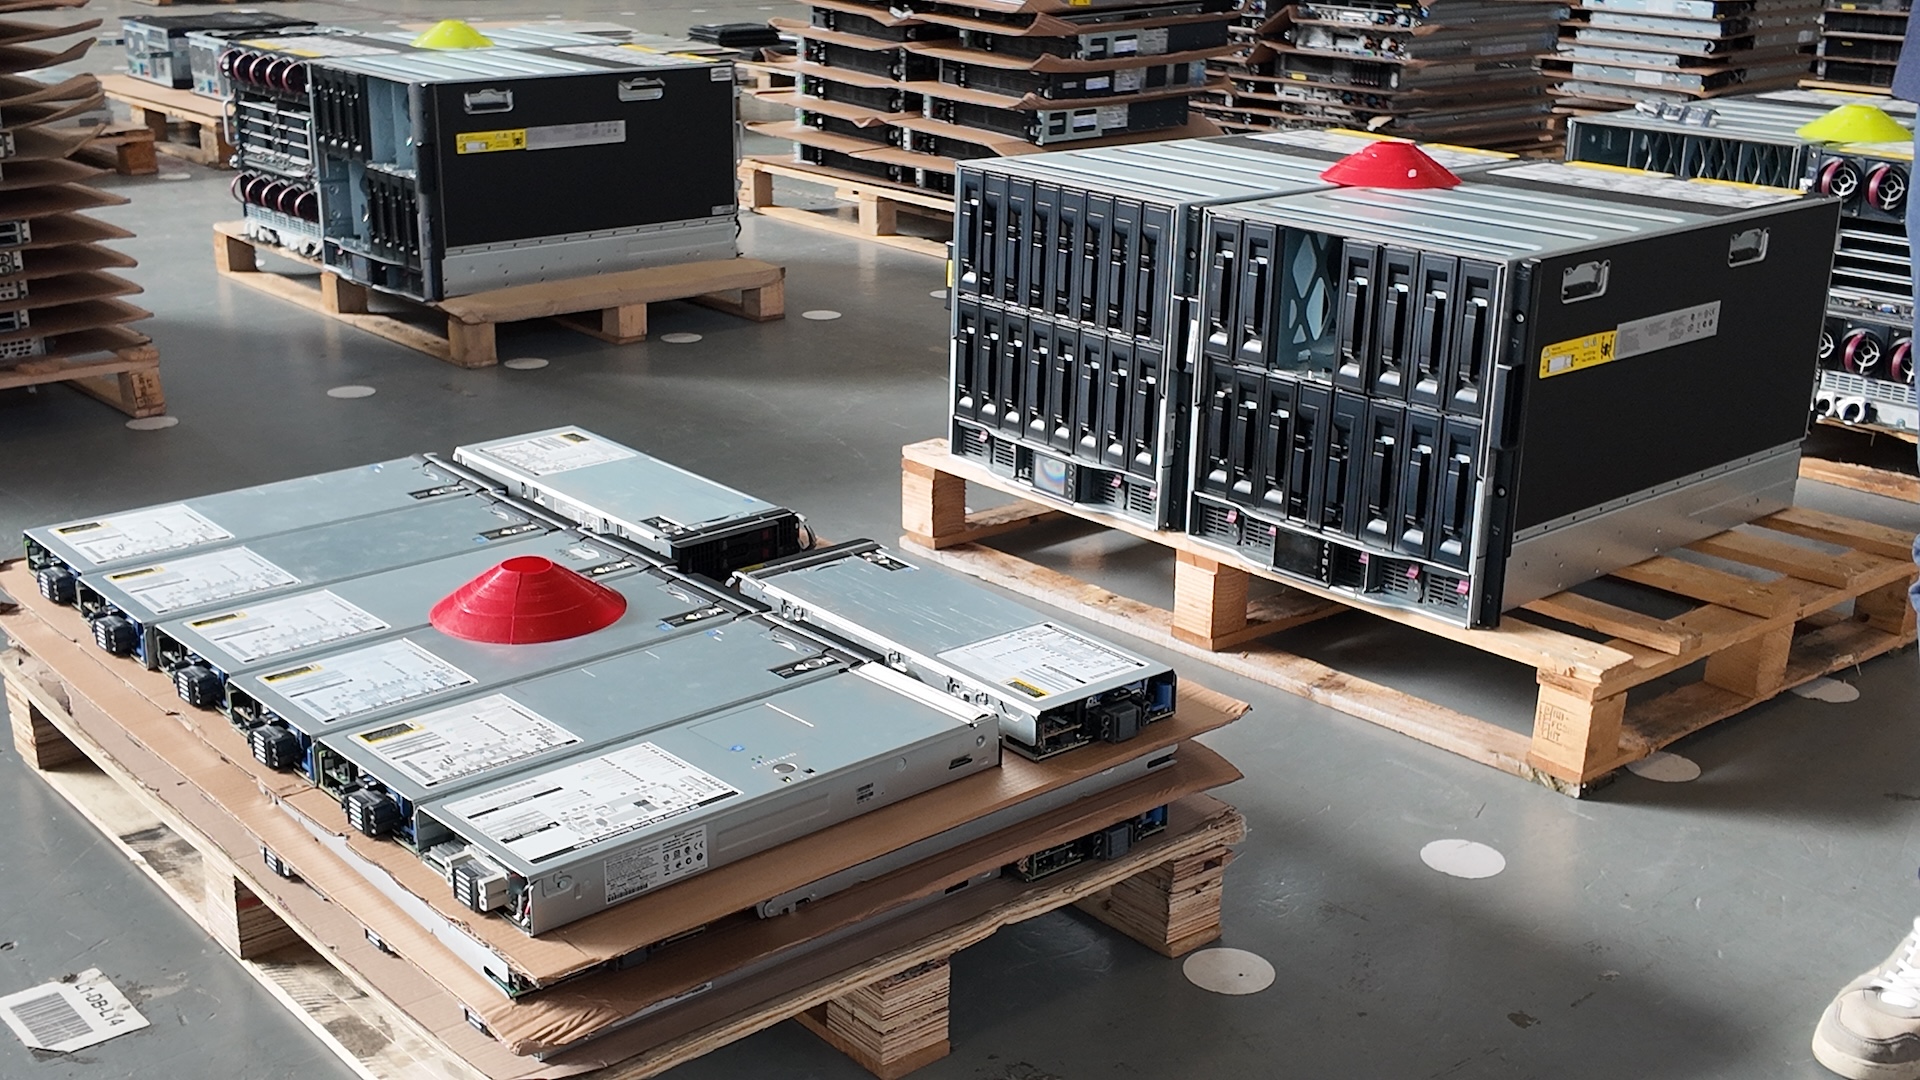 Can tech ever be truly circular? A rising market for refurbished hardware says it can
In-Depth As AI drives compute demand, the confidence in pre-owned tech is proving that circular IT is a business strategy, not just an ESG target
-
 Know your Microsoft 365 data, trust your recovery
How contextual intelligence helps IT teams reduce ROT, protect sensitive content, and govern AI access


-
 A quarter of security vulnerabilities are never fully fixed – and AI is compounding the problem
News A new study warns against delegating flaw fixes to AI when human staff are still struggling to understand what's wrong
-
 Hackers are using patches to create vulnerability ‘maps’ – that means the 'patch and move on' approach needs to end
News Terra Security has spotted a leap in vulnerabilities in patches or otherwise fixed code
-
‘The economics of vulnerability discovery have changed’: NIST wants to modernize the National Vulnerability Database amid AI advances – cyber experts say it needs to be redesigned with machine-speed in mind
News The National Vulnerability Database was designed for human-speed. Advances in AI mean it needs a much-needed overhaul
-
 OpenAI expands 'Daybreak' cyber program: New tools, partnerships, and a cyber-focused GPT-5.5 aim to help 'patch the world'
News The company has added new tools, signed up partners, and released its GPT-5.5-Cyber model more widely
-
 AI is shrinking attack windows, and it’s forcing a complete rethink of cyber resilience – here’s how organizations can prepare
News Commvault has urged companies to improve their business continuity and resilience plans in the face of flaws spotted by AI
-
 Anthropic targets vulnerability detection gains with Claude Security public beta — here's what users can expect
News The Claude Mythos developer is aiming for a more limited approach to cyber tooling for public consumption
-
 Researchers warn millions of RDP and VNC servers are wide open to exploitation
News Researchers at Forescout spotted millions of RDP and VNC servers exposed online
-
 Brace yourselves for a vulnerability explosion, Forescout warns
News AI advances are helping identify software flaws at record pace and scale, but that's not the good news some would think


