26 million CVs were exposed when a recruiting software firm left a misconfigured Azure container open – cybersecurity experts warn it's an easy mistake that's becoming far too common
TalentHook left a misconfigured Azure Blob storage container open, researchers said, leaving jobseekers open to phishing attempts


Security researchers have uncovered a misconfigured recruitment database leaking almost 26 million files, and security experts have warned it's a trend that's becoming far too common.
According to analysis from Cybernews, TalentHook, an online applicant tracking platform connecting HR departments with people looking for work, had left a misconfigured Azure Blob storage container open.
As a result, the resumes of millions of US citizens, including their full names, email addresses, phone numbers, education details, professional details, and employment history were exposed.
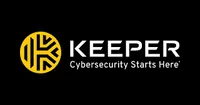
“The detailed personal information in the exposed resumes enables attackers to conduct highly targeted phishing campaigns," the Cybernews team said.
"Email addresses and phone numbers can be used in phishing emails, SMS scams, or fraudulent job offers, tricking individuals into revealing sensitive information such as ID scans or banking details."
The data could be a boon for cybercriminals looking to snare unsuspecting jobseekers, researchers have warned. In recent months, groups such as the North Korean state-sponsored Lazarus group have been specifically targeting jobseekers.
Research earlier this year showed the group has targeted victims using LinkedIn, for example, or by posing as recruiters and approaching targets via email and WhatsApp.
Sharpen up on storage configurations
Tim Mackey, head of software supply chain risk at Black Duck, said the incident shows the huge risks posed by easily overlooked misconfigurations and urged enterprises to sharpen up processes.
"Misconfigured systems, VMs, containers, micro-services, and data stores are nothing new,” he said.
"For example, the sample of the exposed data for this breach masks key identifiable information, such as email addresses and cell phone numbers, indicating that encryption of those elements wasn’t a priority or that an unsecured API was also part of the breach."
Dray Agha, senior manager of security operations at Huntress, echoed Mackey’s comments, noting that incidents like these are becoming increasingly common.
"Misconfigured cloud storage (like the unsecured Azure container in this case) remains an alarmingly common yet preventable issue, especially in sectors handling highly personal information," said Agha.
"Organizations must implement rigorous configuration audits, enforce least-privilege access controls, and conduct continuous monitoring to prevent such massive exposures of stored personal data."
The Cybernews researchers said they have contacted TalentHook, and advised the company to change the access controls to restrict public access and secure the container, and to update permissions to ensure that only authorized users or services have the necessary access.
Make sure to follow ITPro on Google News to keep tabs on all our latest news, analysis, and reviews.
MORE FROM ITPRO
- Employee phishing training is working – but don’t get complacent
- Phishing tactics: The top attack trends
- Hackers are using PDFs to impersonate big brands in a new threat campaign


-
 ‘The claims in the suit are false’: Workday hits back amid lawsuit claiming AI recruitment discrimination
News Is AI hiring discriminatory? A California judge has given the go-ahead for a class action suit against Workday
-
 Been offered a job at Google? Think again. This new phishing scam is duping tech workers looking for a career change
News A new Google Careers phishing scam is targeting tech workers looking for a change of scenery – here's how to stay safe
-
 Workday snaps up AI-powered conversation recruitment platform, Paradox
News Workday will integrate Paradox’s AI-driven candidate experience agent to help deliver talent faster
-
 Tech talent market remains competitive as finance sector sees surge in applicants
News A major investment management firm has seen an increase in tech talent applying for roles with the company, and is still looking to fill 100 more, capitalising on industry-wide tech layoffs
-
 Oracle launches Recruiting Booster platform to improve talent acquisition
News The tech giant aims to help businesses find the right candidates with an automated recruitment platform
-
 Hired by machines: Exploring recruitment's machine-driven future
In-depth As HR begins to incorporate AI, psychometrics, and digital twins, what does this mean for job seekers and businesses alike?
-
 Automated hiring systems are rejecting qualified candidates
News A new Harvard Business School report finds the software tend to hone in on candidates using very specific parameters
-
 TikTok moves into recruitment with 'video resumes'
News Research shows that 18-29-year-olds in the US are more likely to have an active TikTok profile than a LinkedIn account


