-
 Know your Microsoft 365 data, trust your recovery
How contextual intelligence helps IT teams reduce ROT, protect sensitive content, and govern AI access
-
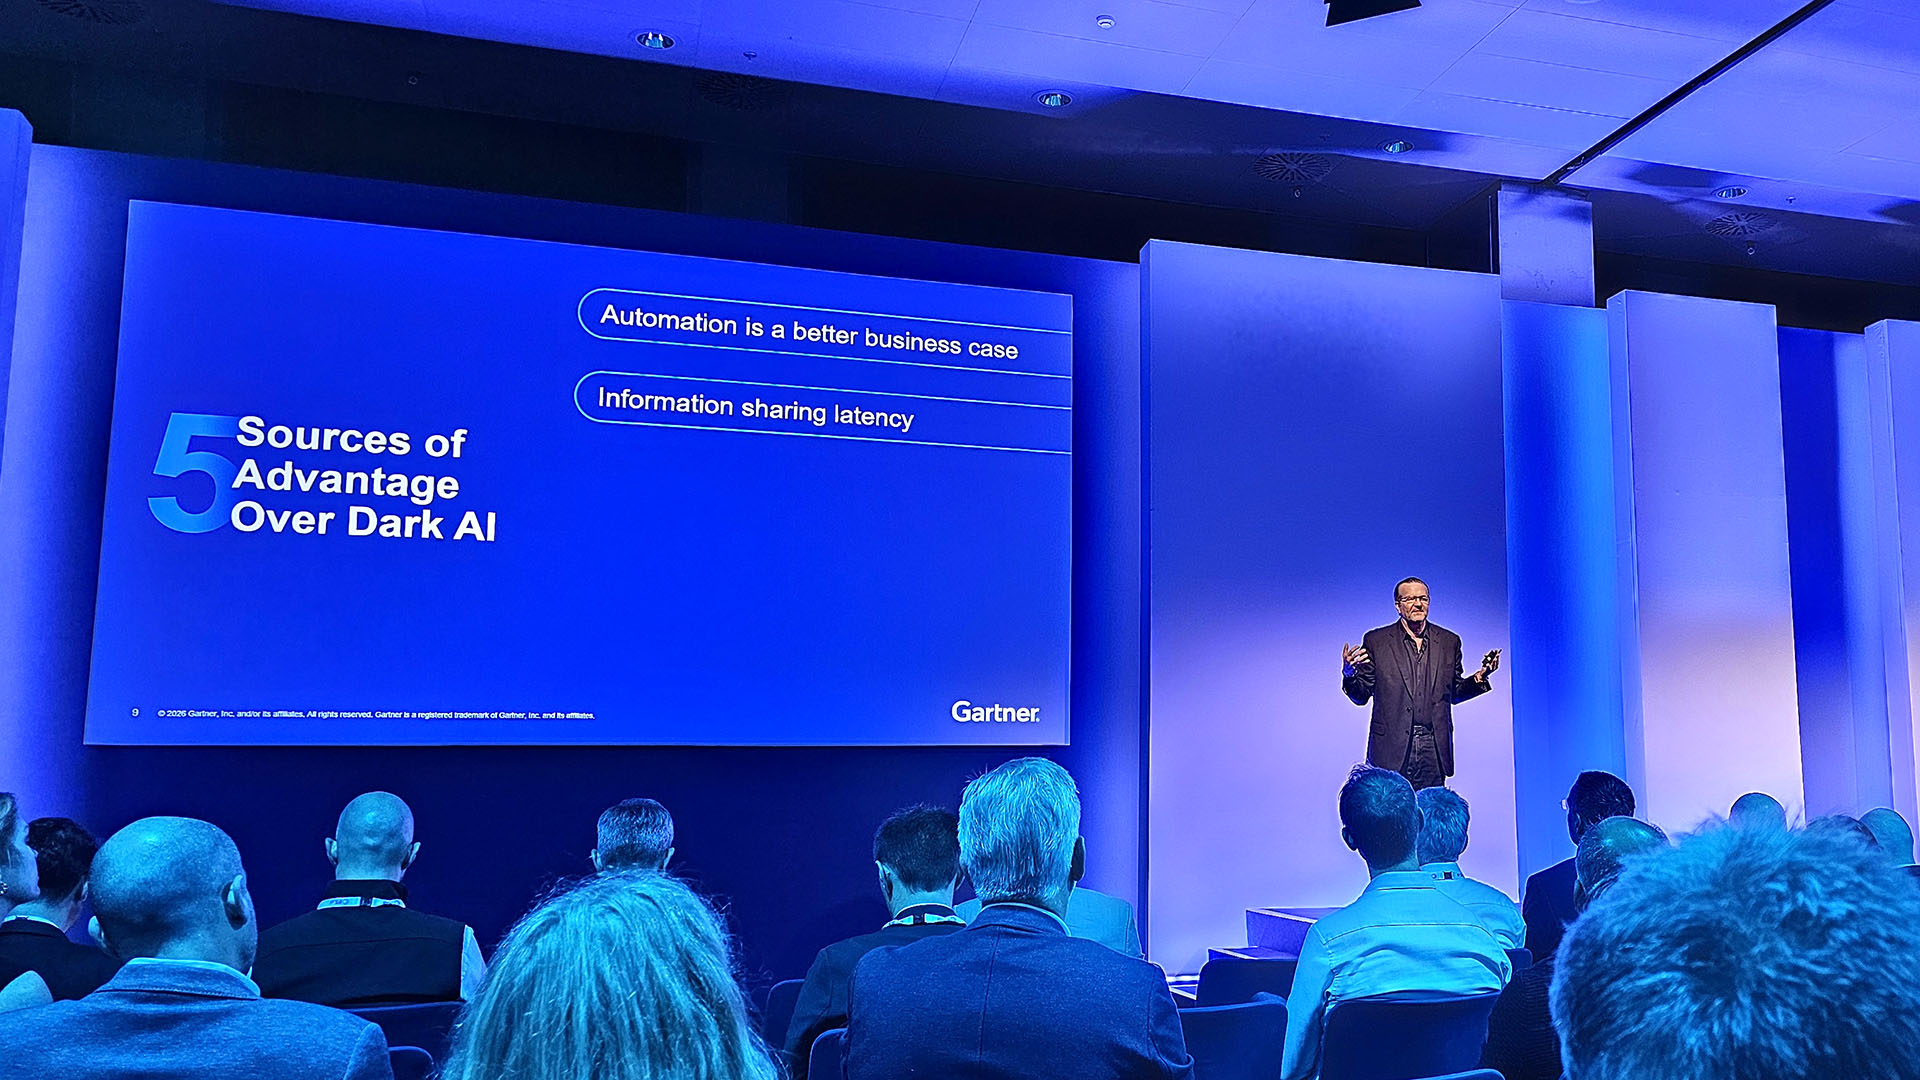 Five ways CISOs can use ‘dark AI’ to their own advantage
In-Depth Vulnerability discovery will explode over the next few years, but CIOs can use AI to beat hackers at their own game


-
 SonicWall issues fixes for seven vulnerabilities – including an SSL-VPN flaw that bypasses MFA
News The vulnerability, which appears to have been exploited in the wild, comes alongside six others
-
 A quarter of security vulnerabilities are never fully fixed – and AI is compounding the problem
News A new study warns against delegating flaw fixes to AI when human staff are still struggling to understand what's wrong
-
 Hackers are using patches to create vulnerability ‘maps’ – that means the 'patch and move on' approach needs to end
News Terra Security has spotted a leap in vulnerabilities in patches or otherwise fixed code
-
 Accenture contractor removed over blunder in lead up to FBI breach
News The contractor is believed to have failed to apply a security patch that would have secured Oracle PeopleSoft
-
‘The economics of vulnerability discovery have changed’: NIST wants to modernize the National Vulnerability Database amid AI advances – cyber experts say it needs to be redesigned with machine-speed in mind
News The National Vulnerability Database was designed for human-speed. Advances in AI mean it needs a much-needed overhaul
-
 Why Microsoft paused Patch Tuesday updates for some Dell devices
News Select devices running Intel Innovation Platform Framework drivers encountered “poor performance”
-
 OpenAI expands 'Daybreak' cyber program: New tools, partnerships, and a cyber-focused GPT-5.5 aim to help 'patch the world'
News The company has added new tools, signed up partners, and released its GPT-5.5-Cyber model more widely
-
 AI is shrinking attack windows, and it’s forcing a complete rethink of cyber resilience – here’s how organizations can prepare
News Commvault has urged companies to improve their business continuity and resilience plans in the face of flaws spotted by AI


