US politicians pass $400 million cyber security bill
Legislation to fund cyber security research and training has faced little opposition from a House of Representatives still reeling from a spate of high-profile attacks.
The US House of Representatives has overwhelmingly passed legislation to provide nearly $400 million in funding for cyber security research over the next four years.
The Cyber security Enhancement Act was passed with a 422-5 majority, and is expected to face little opposition from the Senate. Its overall aim is to speed up the development of a skilled workforce, expand cyber security research and development, and improve public eduction on the matter.
At present, no single US agency is tasked with government cyber security. However, if passed the bill will give the National Science Foundation (NSF) a total of $396 million over four years to fund cyber security research and training aimed at bolstering internet security and better protecting vulnerable computer networks.
The money will be spread between the federal government itself and both the public and private sectors.
A further $94 million will be allocated to funding scholarships in the field of security research, with candidates then required to devote the same number of years as their studies working in the public sector.
Several issues have put US cyber security under the microscope recently, and undoubtedly played a part in the bill's near-unanimous approval. Last month Google revealed that it and several other large corporations had been victims of a wave of cyber attacks originating in China in December, while the websites of nearly 50 House members were hacked into and defaced in the last week.
"As reliance on information technology has increased, so has our vulnerability to cyber attacks," Representative Daniel Lipinski of Illinois, sponsor of the House bill, said in a statement. "This bill will increase the security of vital and personal information by strengthening research partnerships among the federal government, the private sector and colleges and universities," he said.
Sign up today and you will receive a free copy of our Future Focus 2026 report - the leading resource for IT decision-maker insight on priorities and investment areas in AI, security and more.
Also outlined in the bill were plans for the National Institute of Standards and Technology (NIST) to formulate a strategy for national cybersecurity within a year, forming a stronger relationship between government and the security industry and putting in place technical standards for the industry as a whole.
Speaking after the bill was passed, Representative David Wu, a Democrat from Oregon said the US could not "stand by and let the most powerful tool for connecting Americans with each other and the world remain the Wild West of technology".
-
Why the US imposed export controls on Anthropic’s Fable and Mythos models – and why they’ve been liftedNews Anthropic tightens up safeguards and offers expanded early access to US government to end export control issues
-
UK’s ‘Tech Prosperity Deal' with US hits rocky groundNews The US has reportedly threatened to pull out of the deal over the Digital Services Tax and broader economic disagreements
-
‘The UK must position itself as the destination of choice’ in wake of H-1B visa crackdown, tech policy group saysNews The UK has a massive opportunity to capitalize on the US government’s H-1B visa changes
-
The US government's Intel deal explainedNews The US government has taken a 10% stake in Intel – but what exactly does the deal mean for the ailing chipmaker?
-
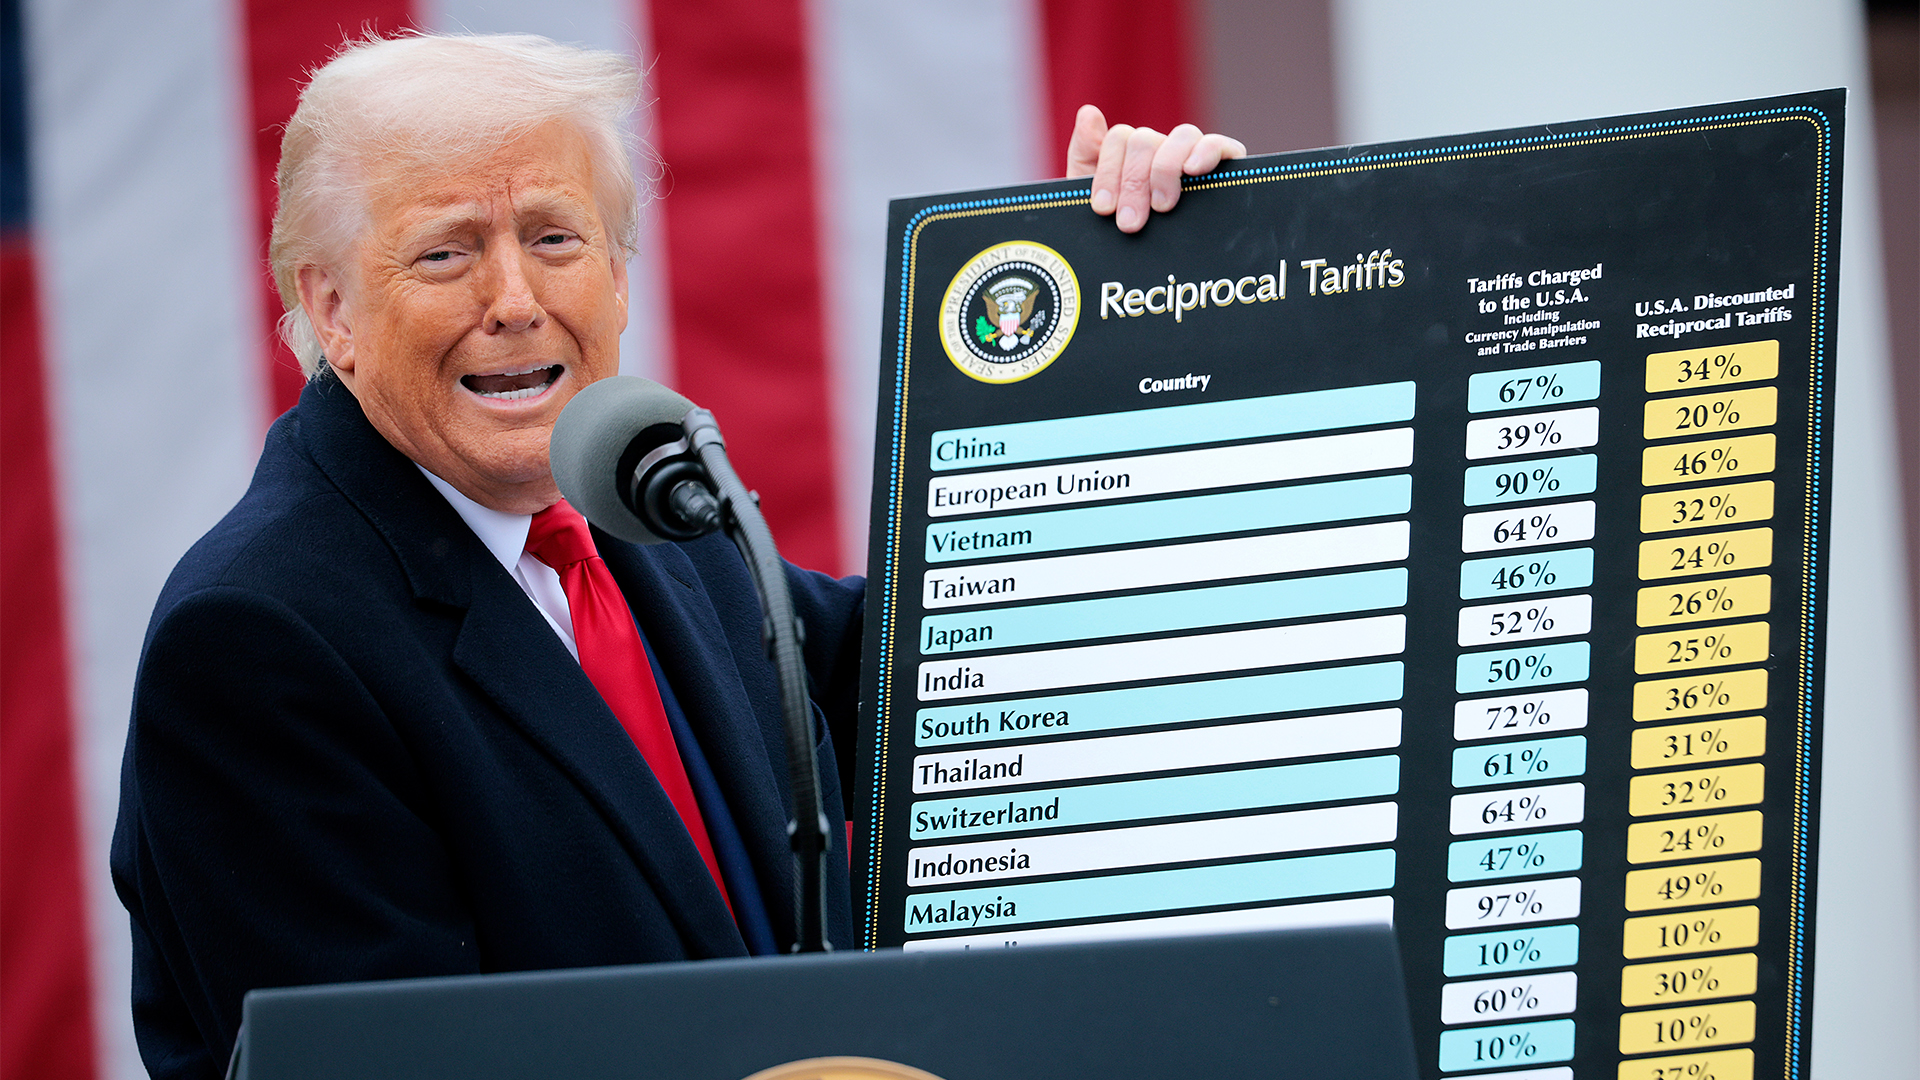
IDC warns US tariffs will impact tech sector spendingNews IDC has warned that the US government's sweeping tariffs could cut global IT spending in half over the next six months.
-
US government urged to overhaul outdated technologyNews A review from the US Government Accountability Office (GAO) has found legacy technology and outdated IT systems are negatively impacting efficiency.
-
Healthcare data breaches are out of control – here's how the US plans to beef up security standardsNews Changes to HIPAA security rules will require organizations to implement MFA, network segmentation, and more
-
The US could be set to ban TP-Link routersNews US authorities could be lining up the largest equipment proscription since the 2019 ban on Huawei networking infrastructure