-
 Beyond the Vulnerability Backlog: Building Risk-Based AppSec Programs
-
 Zero to hero: A blueprint for establishing a security champions program
Whitepaper A buyer's guide for meeting the unprecedented speed and complexity of today's development practices
Whitepaper -
 DevSecOps is dead...or is it?:
Whitepaper A buyer's guide for meeting the unprecedented speed and complexity of today's development practices
Whitepaper -
 Optimizing appsec in the technology sector
-
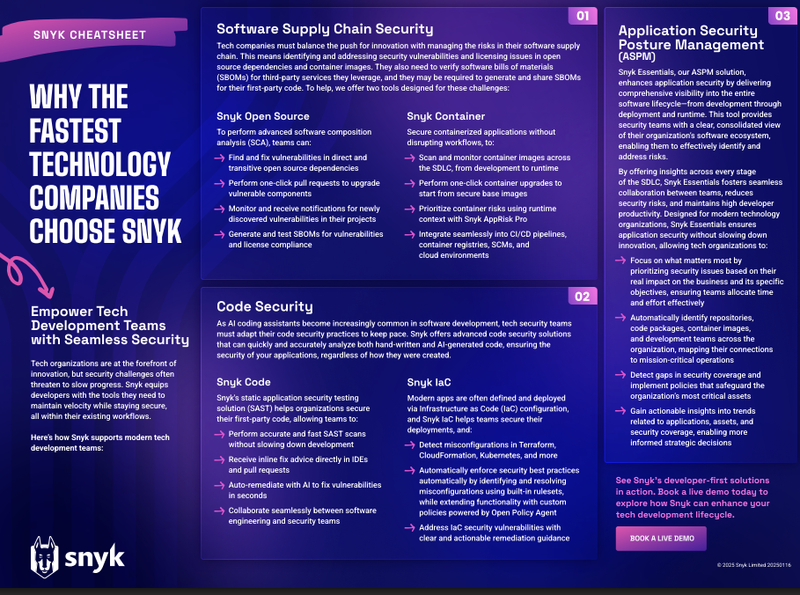 Why the Fastest Technology Companies choose Snyk Cheat Sheet
-
 Criminals target APIs as web attacks skyrocket globally
News More than a third of web attacks target APIs as AI expands attack surfaces and brings new security challenges
News -
 AI is helping bad bots take over the internet
News Automated bot traffic has surpassed human activity for the first time in a decade, according to Imperva
News -
 Security experts issue warning over the rise of 'gray bot' AI web scrapers
News While not malicious, the bots can overwhelm web applications in a way similar to bad actors
News -
 What are business logic vulnerabilities?
Explainer Business logic vulnerabilities let attackers exploit design flaws in software, bypassing security controls to manipulate pricing, authentication, and more
Explainer -
 Red teaming comes to the fore as devs tackle AI application flaws
News Only a third of organizations employ adequate testing practices in AI application development, according to new research, prompting calls for increased red teaming to reduce risks.
News -
 Developers spend 17 hours a week on security — but don't consider it a top priority
News More work on DevSecOps has been identified as a top priority for developer teams
News -
 Organizations urged to act fast after GitHub Action supply chain attack
News More than 20,000 organizations may be at risk following a supply chain attack affecting tj-actions/changed-files GitHub Action.
News


