Zero trust, zero phish
Protecting against deceptive and dangerous link-based attacks

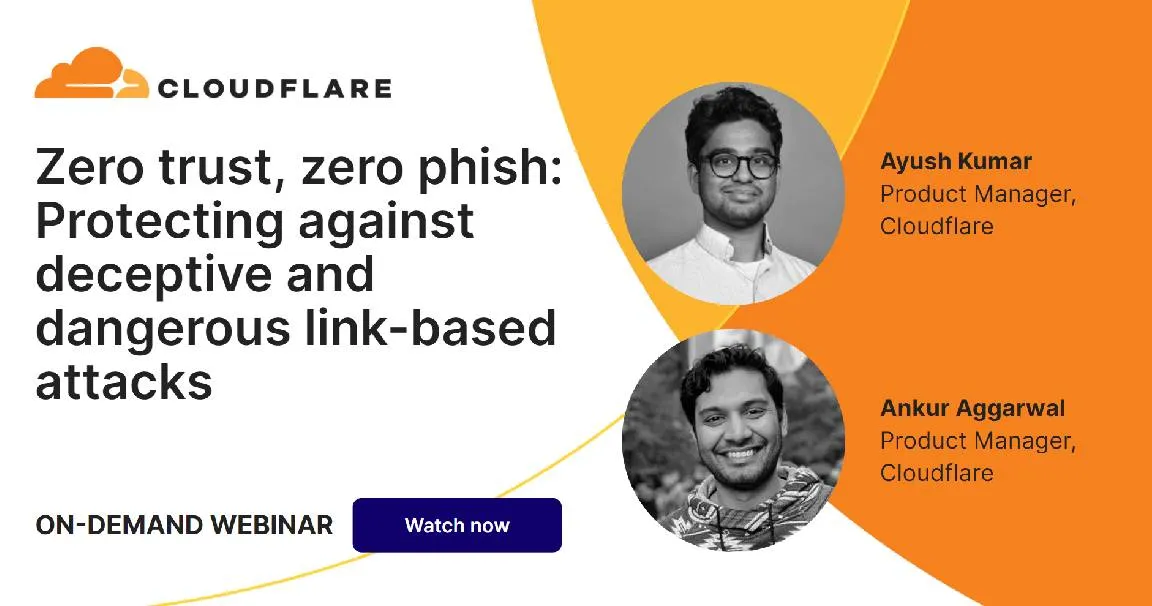
Link-based attacks have become the go-to method for stealing credentials, loading malware/ransomware, and extracting sensitive information. Join this webinar to learn how organizations can proactively insulate their workforce from malicious web content that comes through email, text messages, instant messaging, social media, cloud productivity apps, and more.
As modern phishing attacks become more deceptive, even the best trained security solutions struggle to accurately identify malicious links 100% of the time. Link shorteners further complicate this problem by enabling deferred attacks, where malicious links embedded in emails are activated post-delivery, effectively evading inbound security controls.
While email is still the primary delivery mechanism for malicious links, attackers have expanded their tactics beyond just email, engaging users across various applications used for daily collaboration. This attack technique, known as multi-channel phishing, has emerged as a preferred method for exposing users to a wide range of threats.
Join us to learn more about:
- Why deferred and multi-channel attacks are becoming more popular (and dangerous!)
- How attackers target users across various applications used for daily collaboration
- How to thwart link-based attacks that bypass traditional security controls
- How Cloudflare’s proprietary isolation technology protects users without them knowing
Provided by Cloudflare
-
 Opengear pens first European distribution deal with Ingram Micro
News The agreement will expand the availability of the vendor's network resilience solutions across the continent
-
 Enterprise AI is moving beyond training; infrastructure needs to support this evolution
Storage and other data center infrastructure form the heart of business transformation, but not all solutions are up to the job


-
 Microsoft takes down ‘EvilTokens’ hacker service that used AI to ‘decide who to target, who to impersonate, and how to most effectively exploit’ victims
News In just six months, the EvilTokens phishing as a service platform hit thousands of organizations worldwide
-
 ‘Cyber criminal groups suffer from the same security weaknesses they routinely exploit’: ShinyHunters claims it hacked Clop ransomware rival
News An attack on the cyber crime gang could prove dangerous for previous victims of data leaks, experts have warned
-
Cyber criminals are adapting ASCII smuggling for mass phishing campaigns
News Usually known for its use in prompt injection attacks, ASCII smuggling is now being used to evade spam filters on email platforms
-
 Expired domains are a goldmine for hackers – and some cyber crime groups are investing millions in 'dropcatch' scams to deliver malware
News Tens of thousands of so-called 'dropcatch' domains are being registered every day
-
 Delta Airlines flight Wi-Fi tampered with after DEF CON conference
News A rogue network named 'Delta WiFi Fast' was created in an apparent in-flight phishing attack
-
 NCSC issues alert over 'zero-click' phishing campaign hitting enterprises
News Ukrainian organizations were used to test new zero-click techniques employed by Russian hackers
-
 Companies are still paying ransoms to cyber criminals despite official advice
News A Proofpoint survey found evolving ransomware techniques and the use of AI is exacerbating the situation for victims
-
 This one cyber crime group accounted for nearly a fifth of all ransomware attacks in June
News The Gentlemen, a ransomware a service operator, now accounts for 17% of published attacks


