
-
 The hidden cost of AI is now governance
In-depth There's a growing burden of policies, approvals, auditing, data controls, and human oversight required to deploy enterprise AI safely and effectively
-
 AI agents are gaining employee-level access. How partners can stop over-privileged automation
Industry Insights How partners can rein in over-privileged agents before access becomes a risk


-
 EU can't afford sovereign cloud, research claims
Citing costs that it claims have been overlooked, CCIA Europe is predicting a €115 billion bill.
-
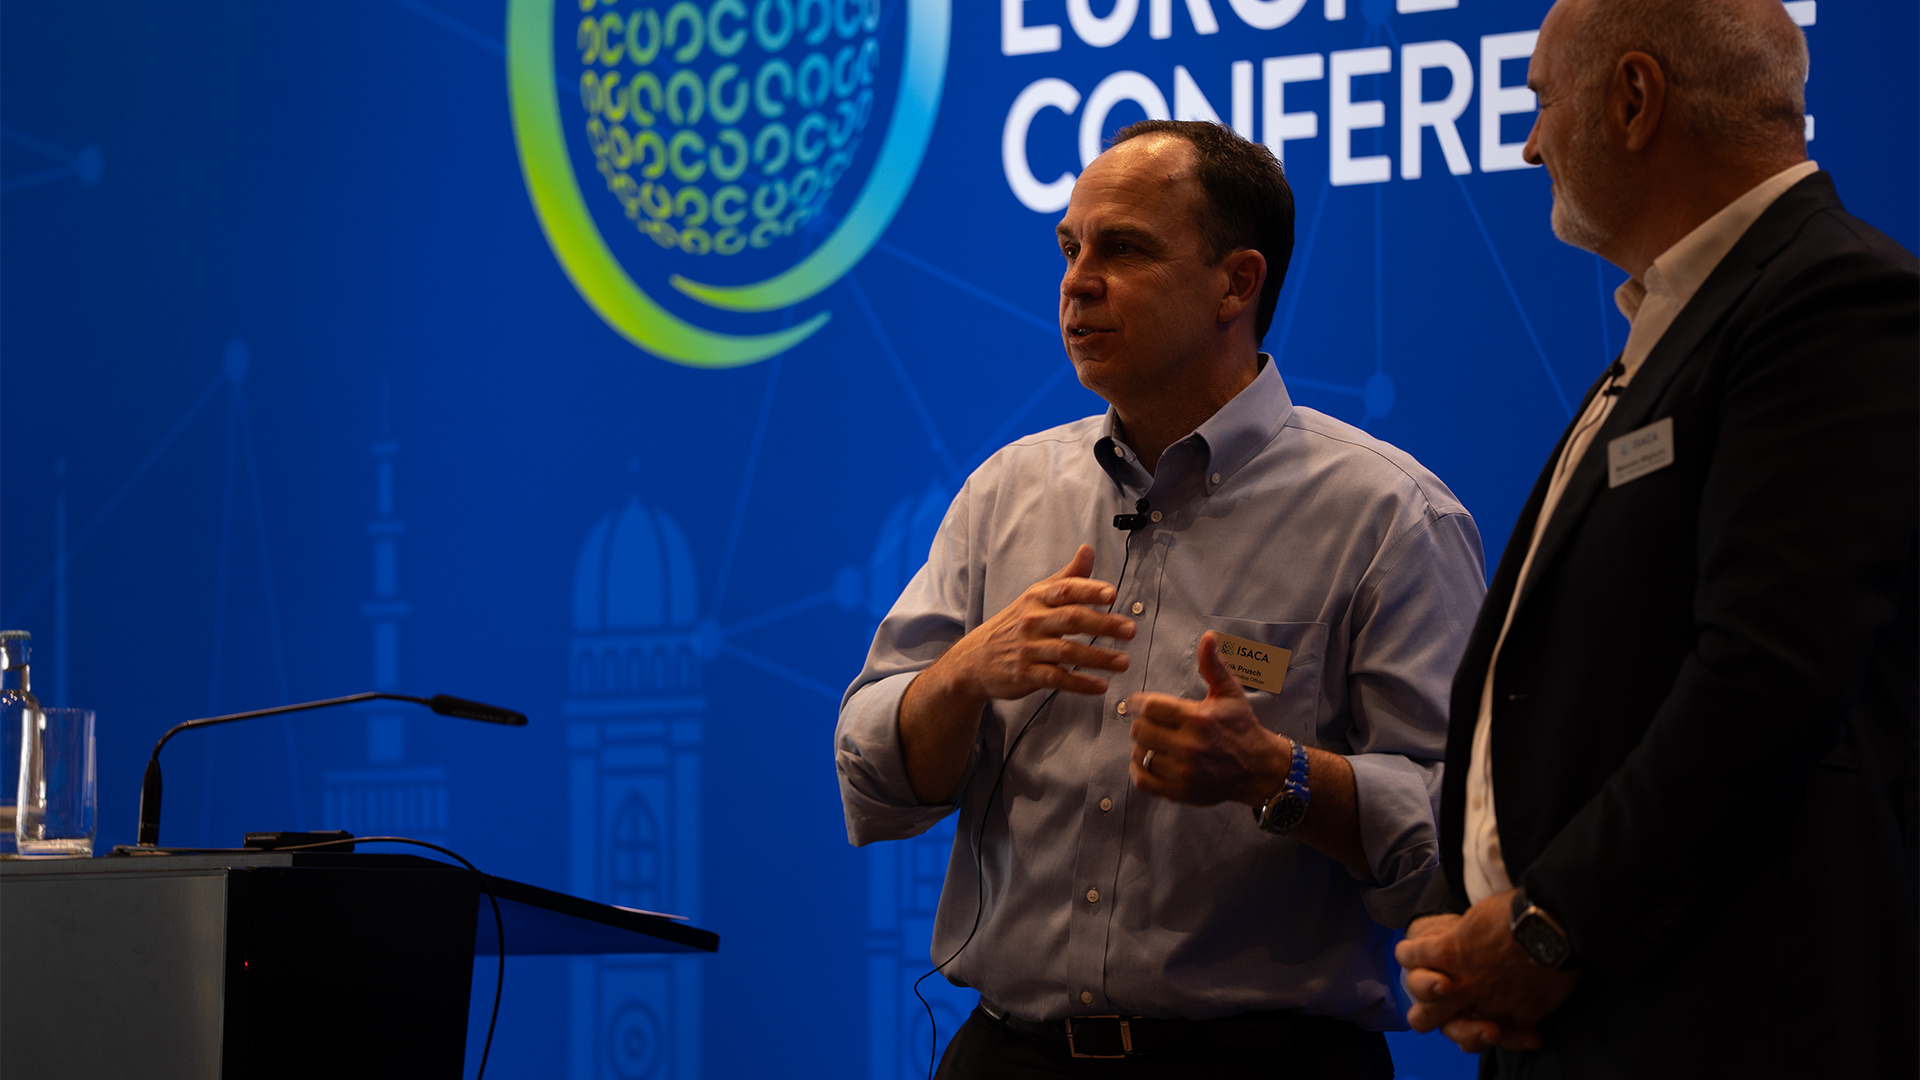 ISACA CEO says AI compliance will be like 'SOX on steroids'
News Businesses will need to do far more work in far less time to meet stringent regulations
-
 Three things you need to know about the new EU AI Act rules
News From this week, organizations operating in the EU have a new set of obligations around AI content and transparency
-
 Startup founders lament 'regulatory friction' despite EU simplification efforts
News Entrepreneurs are spending a fortune on compliance, and it’s forcing some to consider relocating
-
 AWS says cloud market gatekeeper designation risks ‘deterring European investment and innovation’ as EU regulators plot competition crackdown
News Gatekeeper designation under the legislation would force AWS and Microsoft to make concessions
-
‘This closes a gap that has caused real uncertainty in the market’: Changes to EU AI Act implementation deadlines welcomed by industry
News New implementation deadlines for the EU AI Act could help remove “genuine friction” for European companies
-
European Commission approves data flows with UK for another six years
News The European Commission says the UK can have seamless data flows for another six years despite recent rule changes
-
Three things you need to know about the EU Data Act ahead of this week's big compliance deadline
News A host of key provisions in the EU Data Act will come into effect on 12 September, and there’s a lot for businesses to unpack.


