Chinese tech experts who find any flaws in computer security will be required to tell the Chinese government. Furthermore, the government will forbid them from selling that knowledge for profit.
That’s according to new rules further tightening the Chinese Communist Party’s control over digital information, as the Associated Press reported.
These rules, which take effect September 1, will ban private-sector cyber security experts who find zero-day or previously unknown security weaknesses from selling that information to police, spy agencies, or companies.
China’s government is increasingly sensitive about its control over information on China’s people and economy.
2021 IBM Security X-Force Insider Threat Report
Top discovery methods and recommendations for insider attacks
For example, Chinese companies are barred from storing data about Chinese customers outside of China. Banks and other entities deemed sensitive must use only Chinese-made security products wherever possible. Foreign vendors that sell routers and some other network products in China must disclose to regulators how any encryption features work.
Under the Cyberspace Administration of China's new cyber security rules, anyone in China who finds a vulnerability must tell the government. The government will then decide what repairs to make.
No one may “collect, sell or publish information on network product security vulnerabilities,” according to the rules. Also, no information can be given to “overseas organizations or individuals” other than the product’s manufacturer.
The ruling party’s military wing, the People’s Liberation Army (PLA), is a leader in cyber warfare technology alongside the US and Russia. US prosecutors have previously charged PLA officers with hacking American companies to steal technology and trade secrets.


-
 The UK is betting big on the power of open source AI
News The government wants to encourage open source developers to help improve public services
-
 UK’s AI Hardware Plan welcomed by industry as government bets big on domestic chip capabilities
News With a focus on British chip firms, the plans include £750 million for the development of a new national AI supercomputer
-
 UK government calls on firms to sign Cyber Resilience Pledge as security sector booms
News With new figures showing a boom in the country's cybersecurity sector, the government calling on businesses to make the most of the industry’s expertise
-
 UK Government says it’s ‘cut cyber attack fix times by 84%’ with new vulnerability monitoring service
News A new scanning service spots weaknesses in government DNS records for 6,000 UK public sector bodies
-
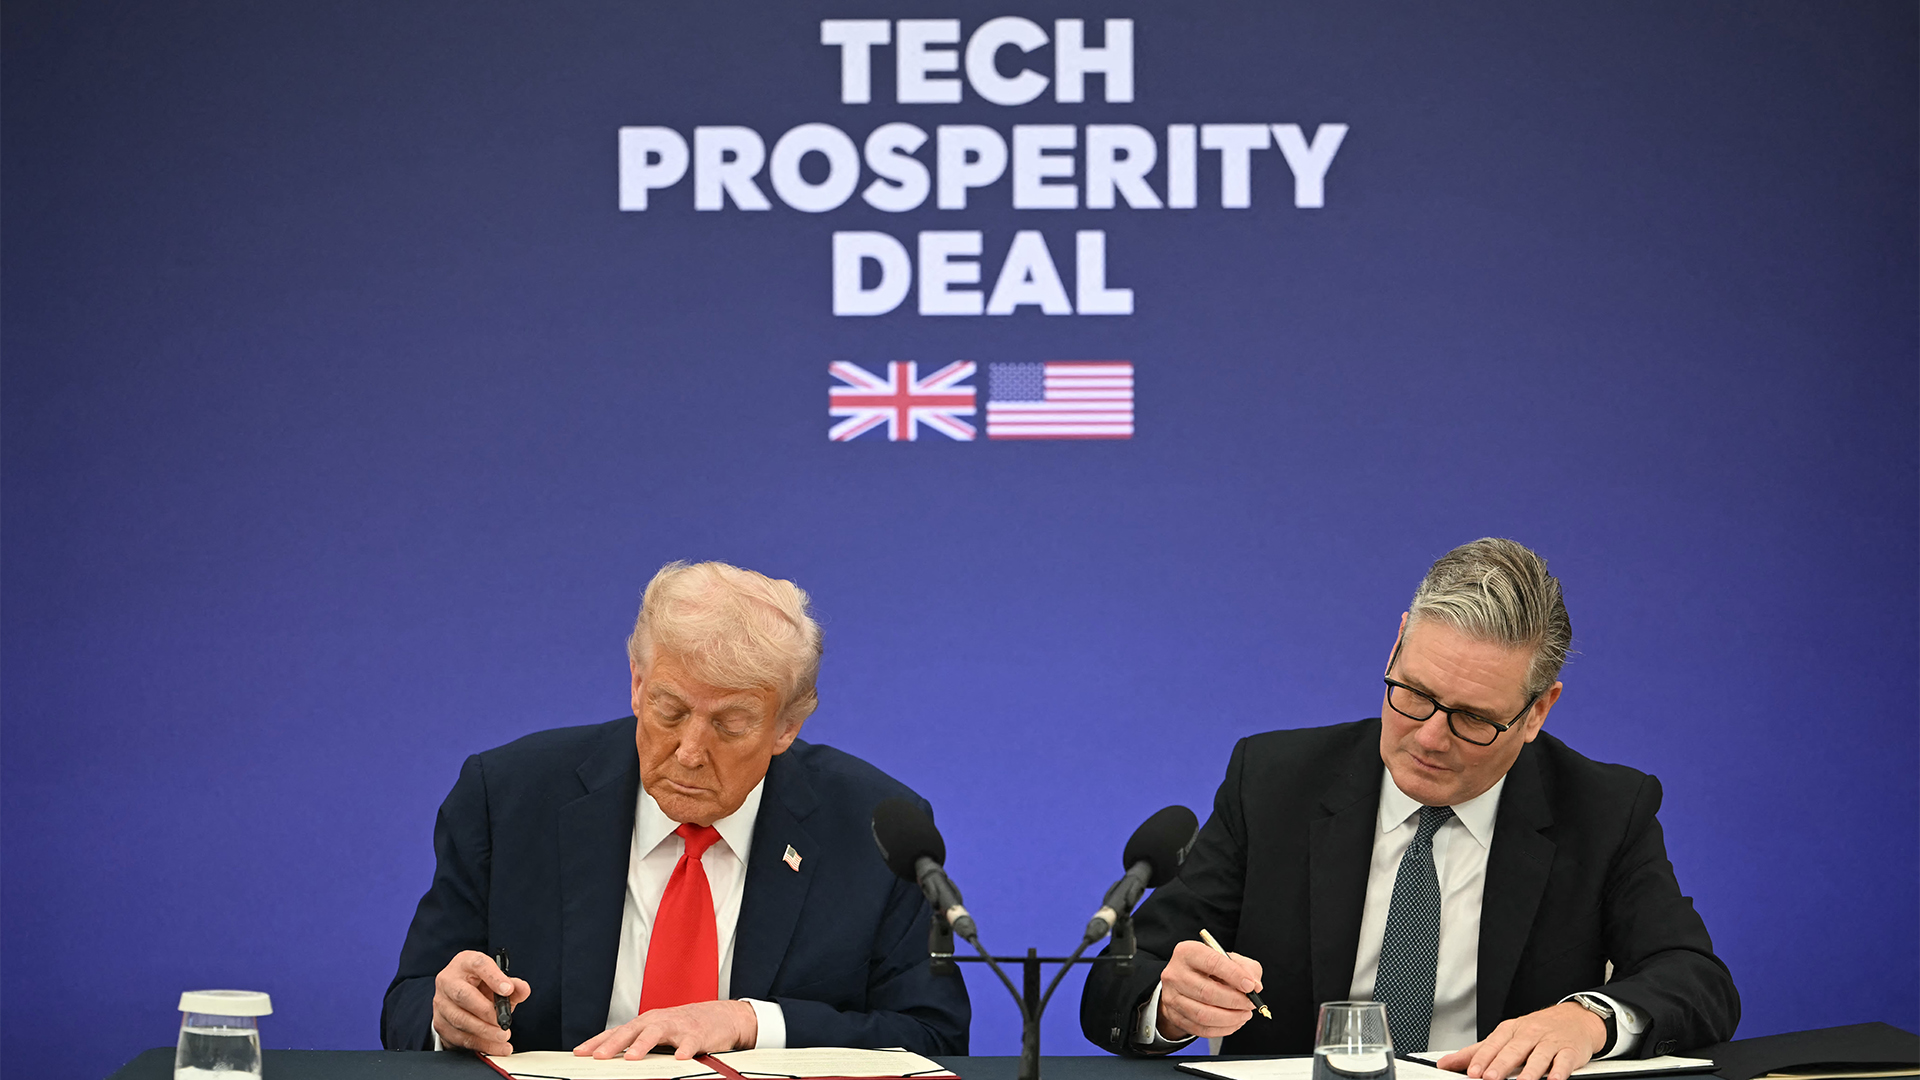 UK’s ‘Tech Prosperity Deal' with US hits rocky ground
News The US has reportedly threatened to pull out of the deal over the Digital Services Tax and broader economic disagreements
-
 ‘Hugely significant’: Experts welcome UK government plans to back down in Apple encryption battle – but it’s not quite over yet
News Tulsi Gabbard, US director of national intelligence, has confirmed the UK plans to back down on plans that would see Apple forced to create a "back door" for authorities.
-
 The UK government is working with Meta to create an AI engineering dream team to drive public sector adoption
News The Open-Source AI Fellowship will allow engineers to apply for a 12-month “tour of duty” with the government to develop AI tools for the public sector.
-
 ‘A huge national security risk’: Thousands of government laptops, tablets, and phones are missing and nowhere to be found
News A freedom of information disclosure shows more than 2,000 government-issued phones, tablets, and laptops have been lost or stolen, prompting huge cybersecurity concerns.


